Risk management. Finally simple.
One platform for the whole cycle: identify, assess, treat and monitor, from the identified risk to proof that the control works.
Before.
Risks in scattered spreadsheets, controls that exist only on paper and board reporting that takes weeks.
Now.
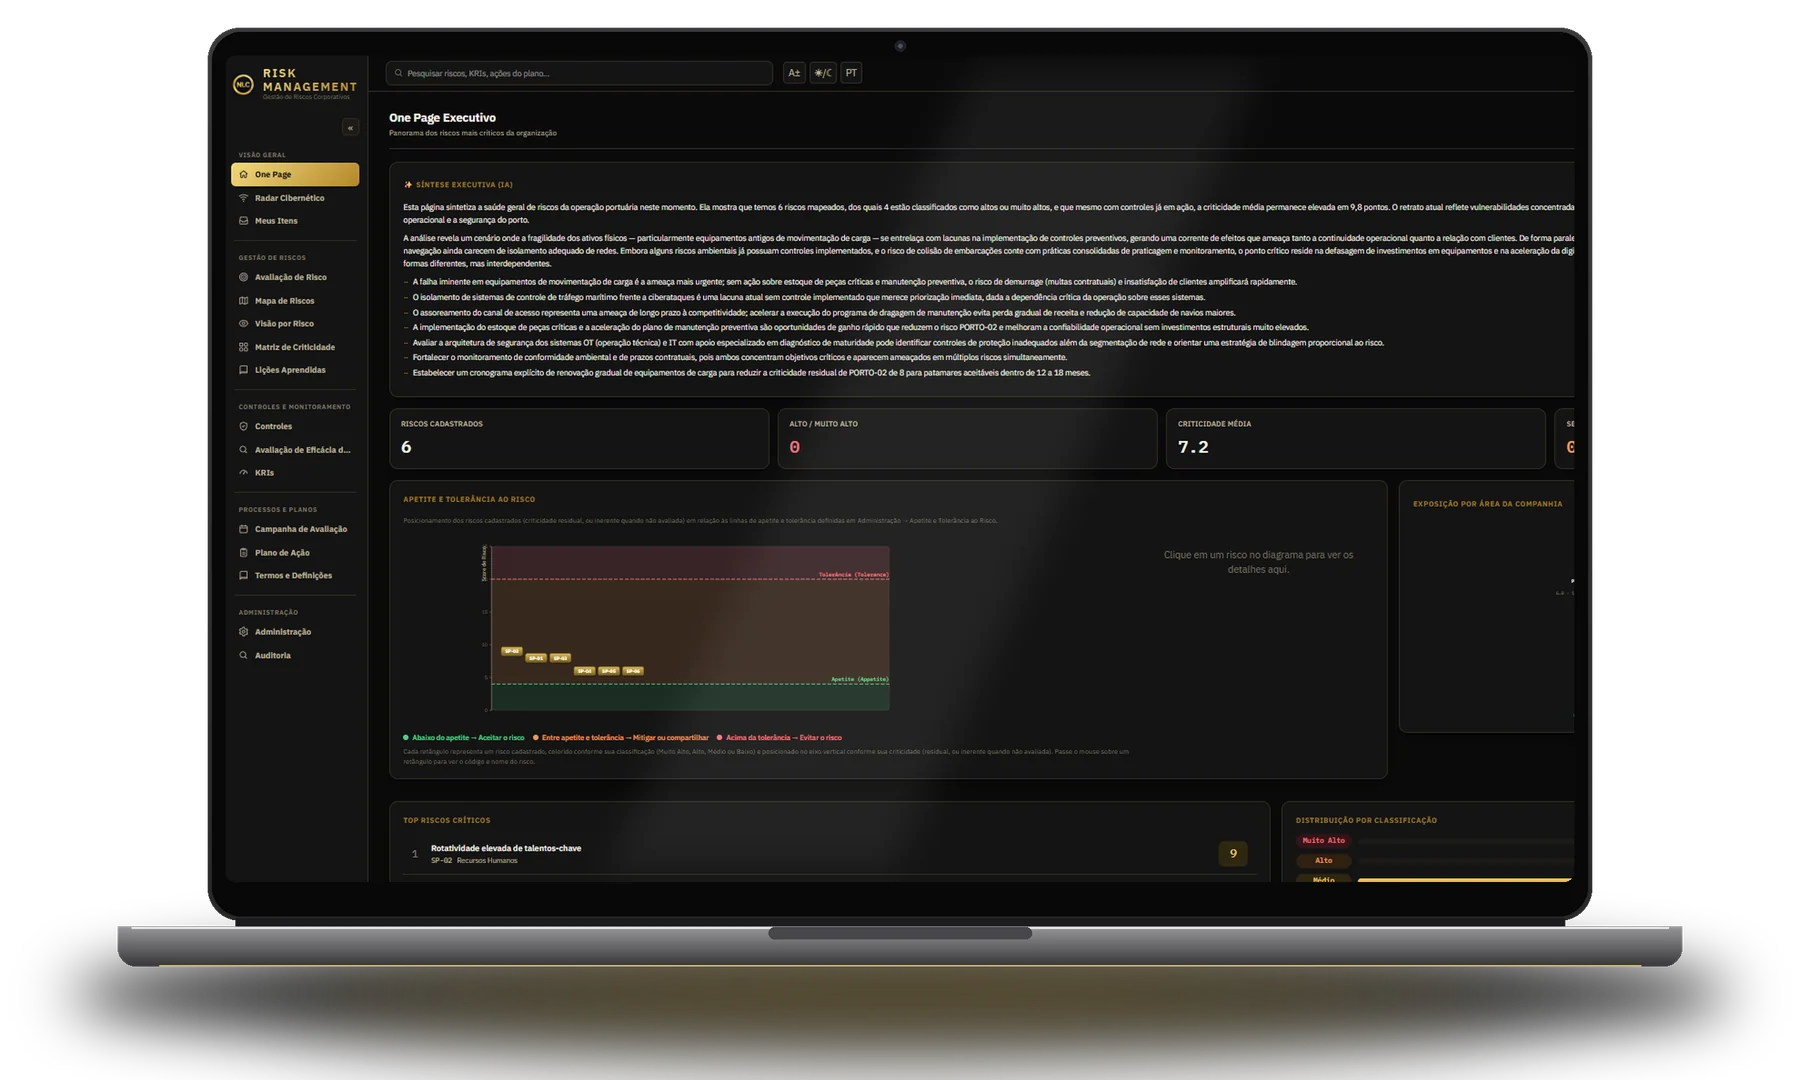
A single platform with COSO and ISO 31000 built in, full traceability and AI agents that write the summaries.
After.
Leadership sees the business's real exposure every day, not once a year.
You know these pains. We built the answer.
Hours lost in spreadsheets
Consolidating risks, controls and plans by hand, every cycle.
Prohibitive pricing
GRC tools that cost more than the risk they manage.
Complexity
Tools nobody uses without a consultant.
Months of waiting
Long rollouts before the first result.
Manual reporting
Weeks to build the board pack.
Controls on paper
Controls that exist but are never tested.
One wrong cell. Billions at stake.
JPMorgan · London Whale · 2012
Losses from a risk model run on spreadsheets.
Fidelity Magellan
A missing minus sign.
TransAlta
A copy-and-paste error.
Audited spreadsheets
Contained errors (Panko).
Sources: JPMorgan Task Force Report (2013) · EuSpRIG · R. Panko, University of Hawaii.
Six fronts. One platform.
Single base, real time, COSO, owner and deadline, and cybersecurity in the same register as enterprise risk.
Identification & Assessment
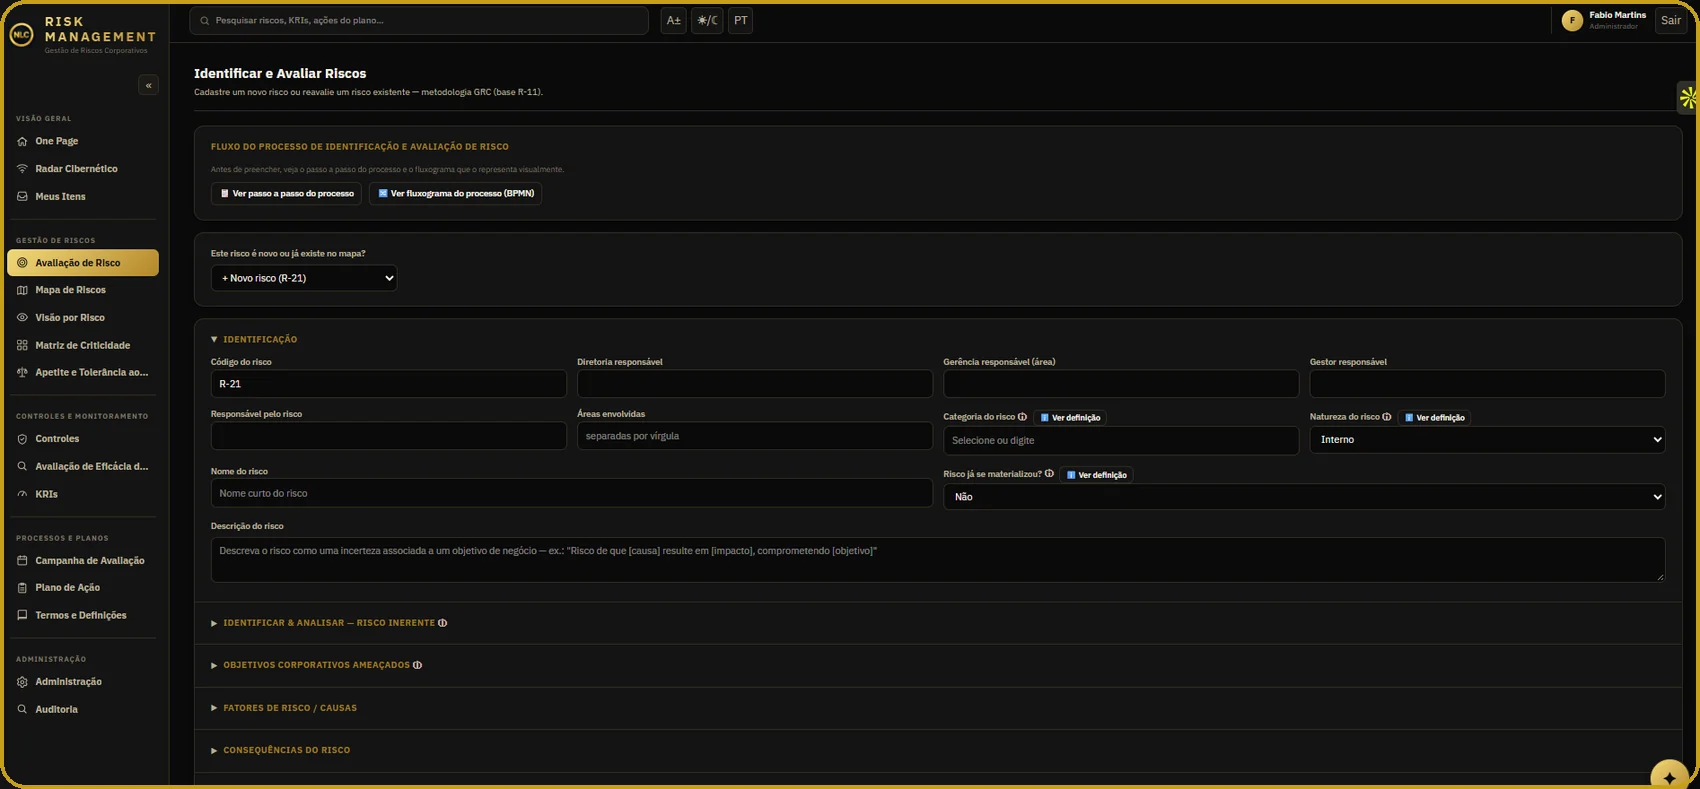
AI agents, Bow-Tie and criticality matrix.
Executive One Page
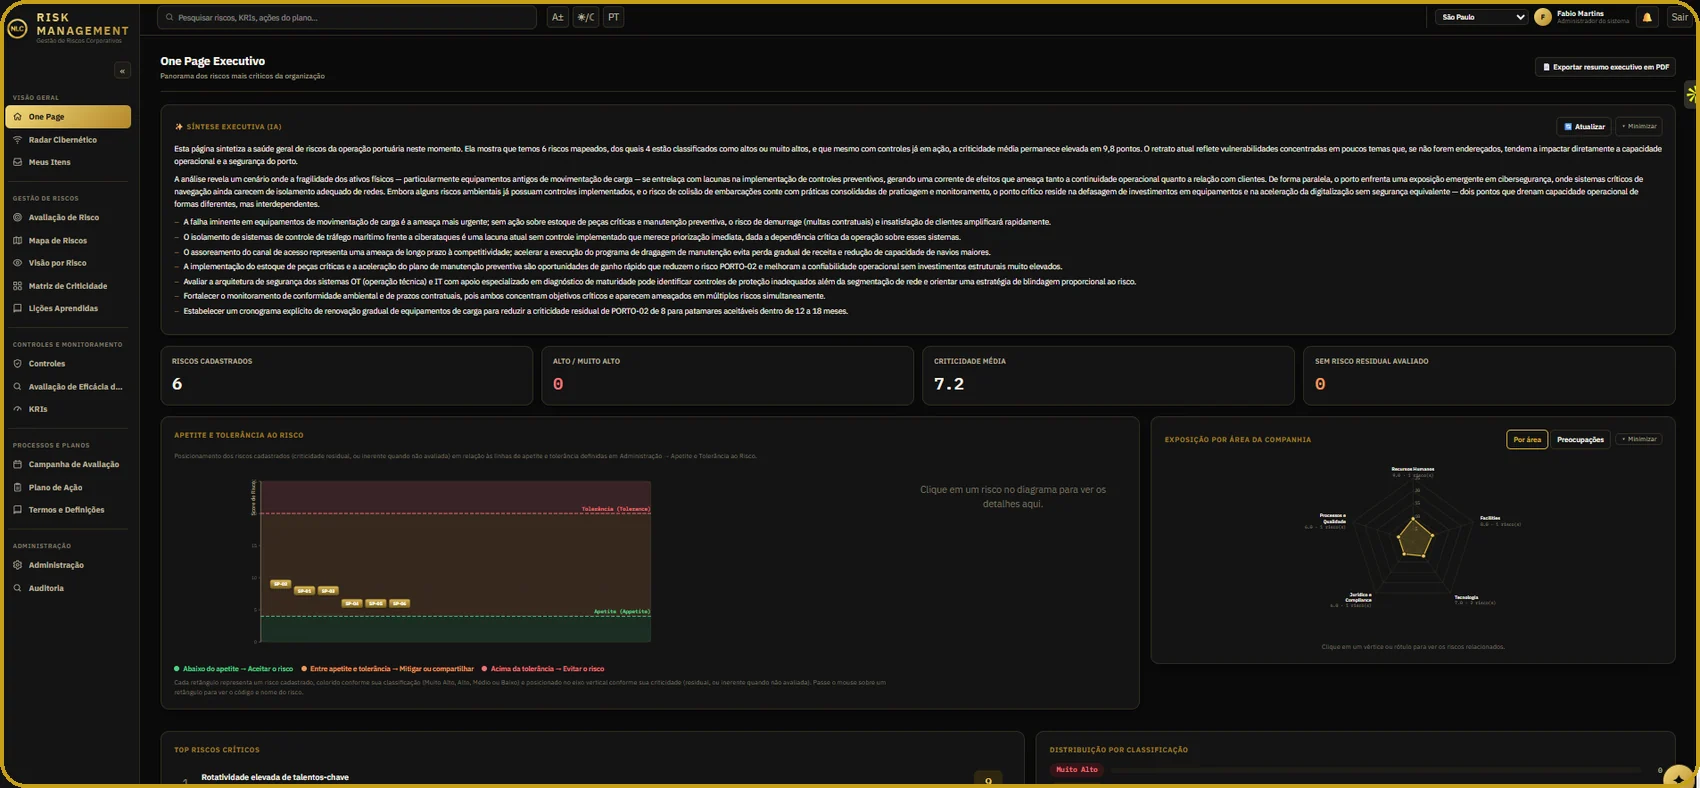
Appetite, objectives and AI agent summary.
Internal Controls
COSO: design and effectiveness.
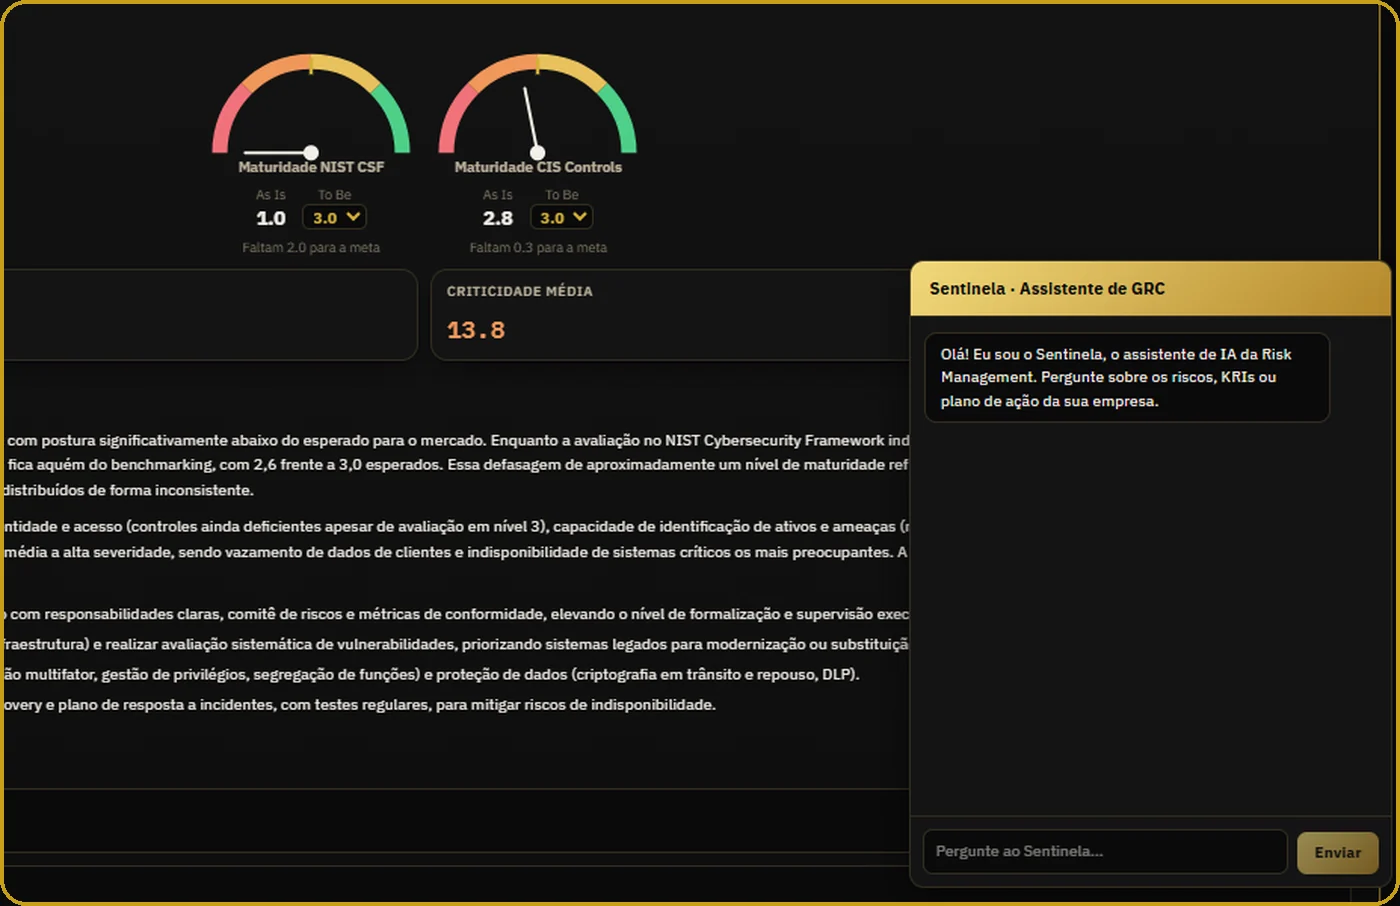
Cyber Radar
NIST CSF 2.0 and CIS Controls.
Action Plan
Owner, deadline and My Items.
KRIs & Appetite
Limits, alerts and tolerance.
AI agents across the risk cycle.
AI agents draft, suggest and summarize. The decision is always yours.
Risks from files and minutes
Upload documents and minutes: AI agents identify and propose risks.
Sentinel, the assistant
Ask about anything on screen, in natural language.
Risk description
Drafted by AI agents from a few words.
Causes and consequences
Suggested for you to validate.
Controls and contingency
Proposed controls and contingency plan.
Executive summaries
One Page, controls and plans in board-ready language.
Nothing enters the register without your approval. Illustration, fictitious documents and risks.
Every screen. A purpose.
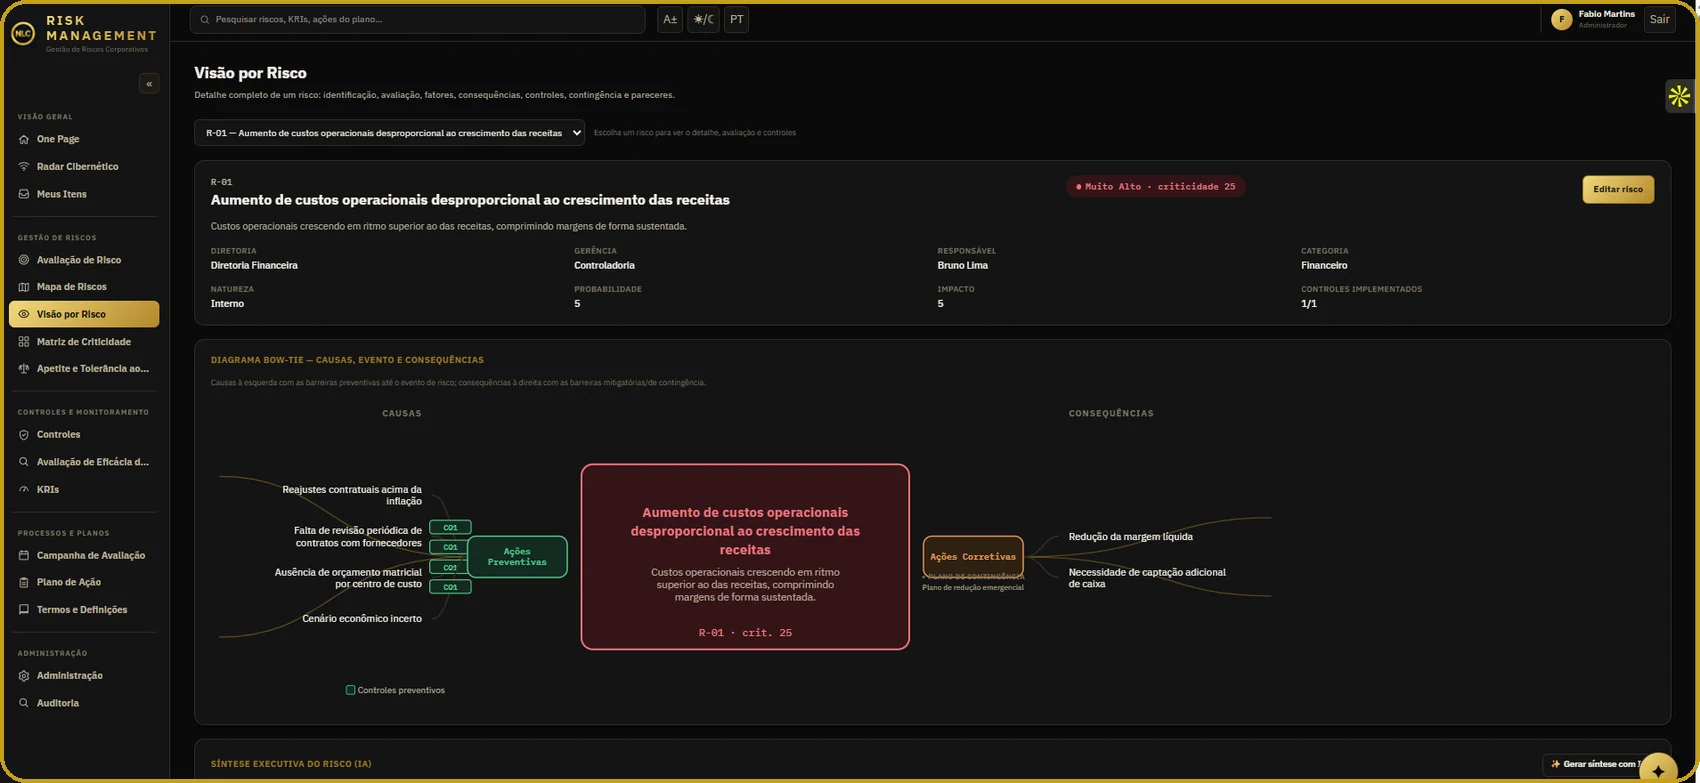
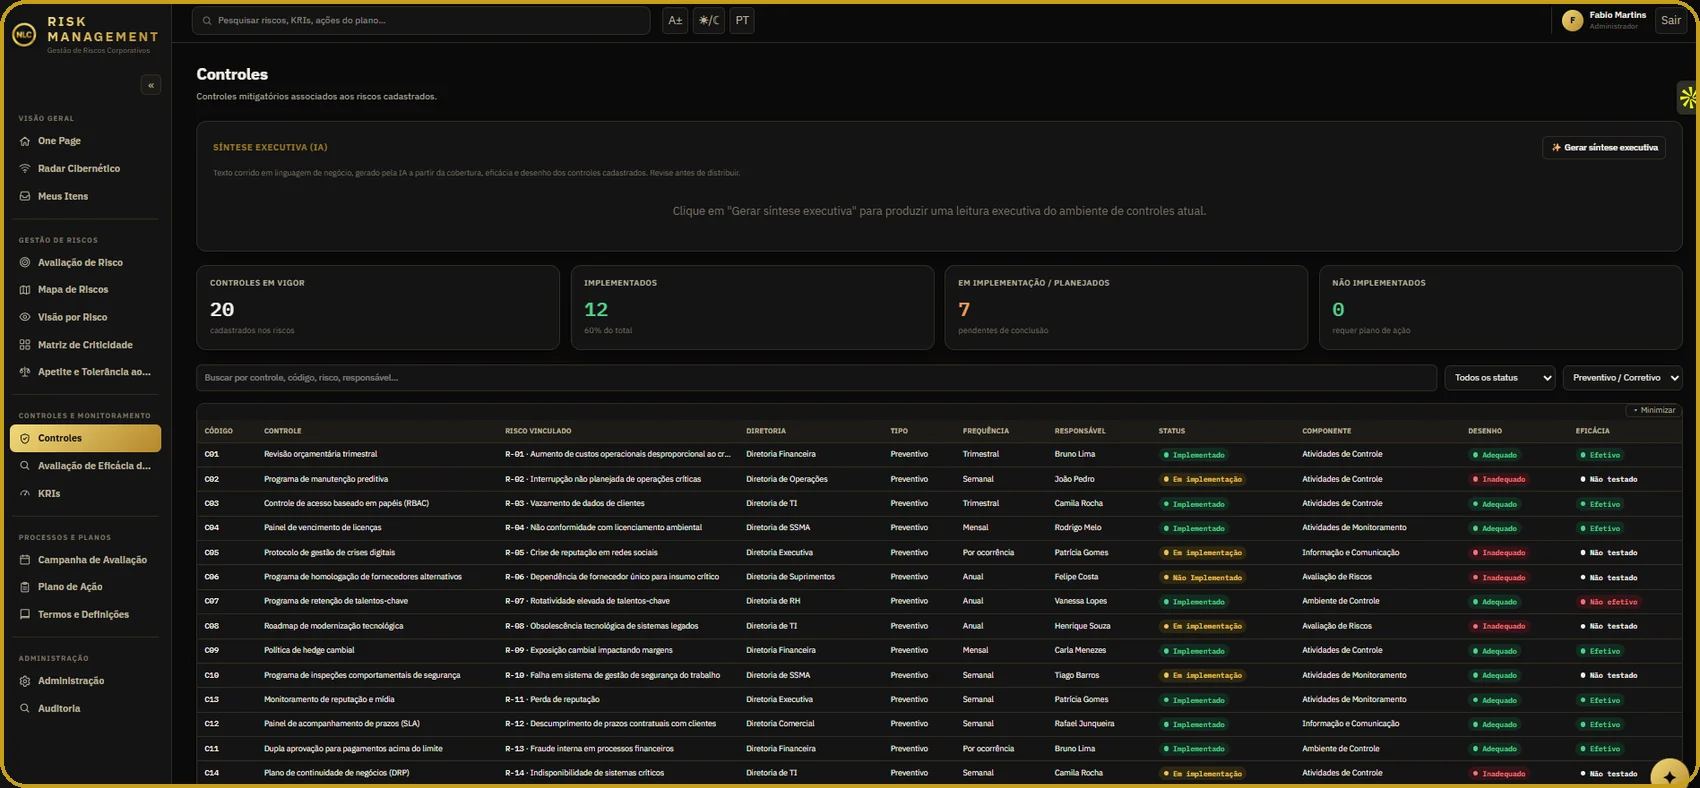
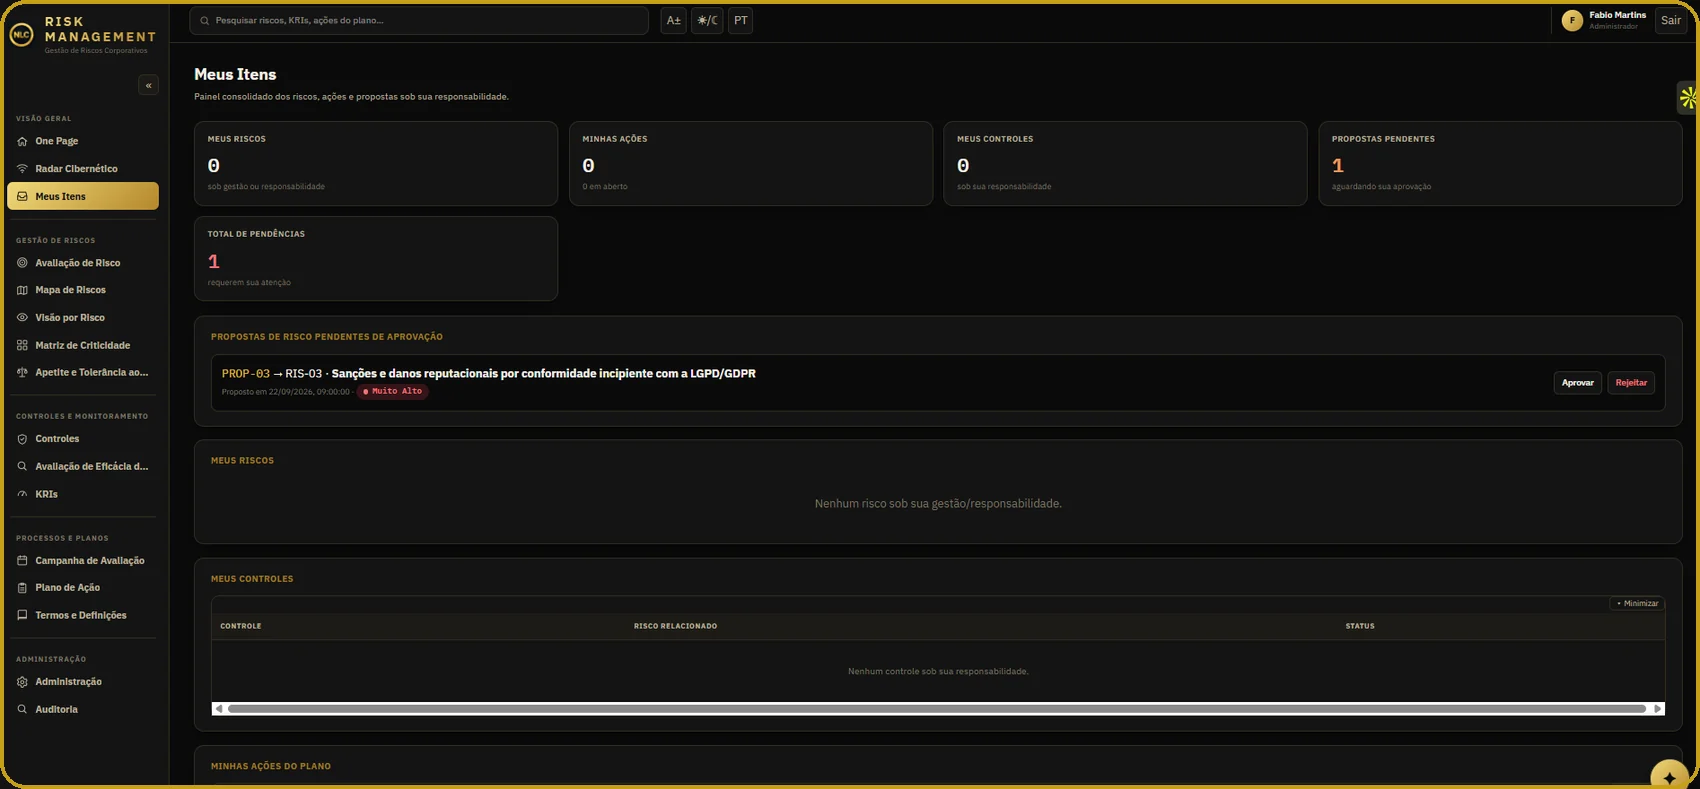
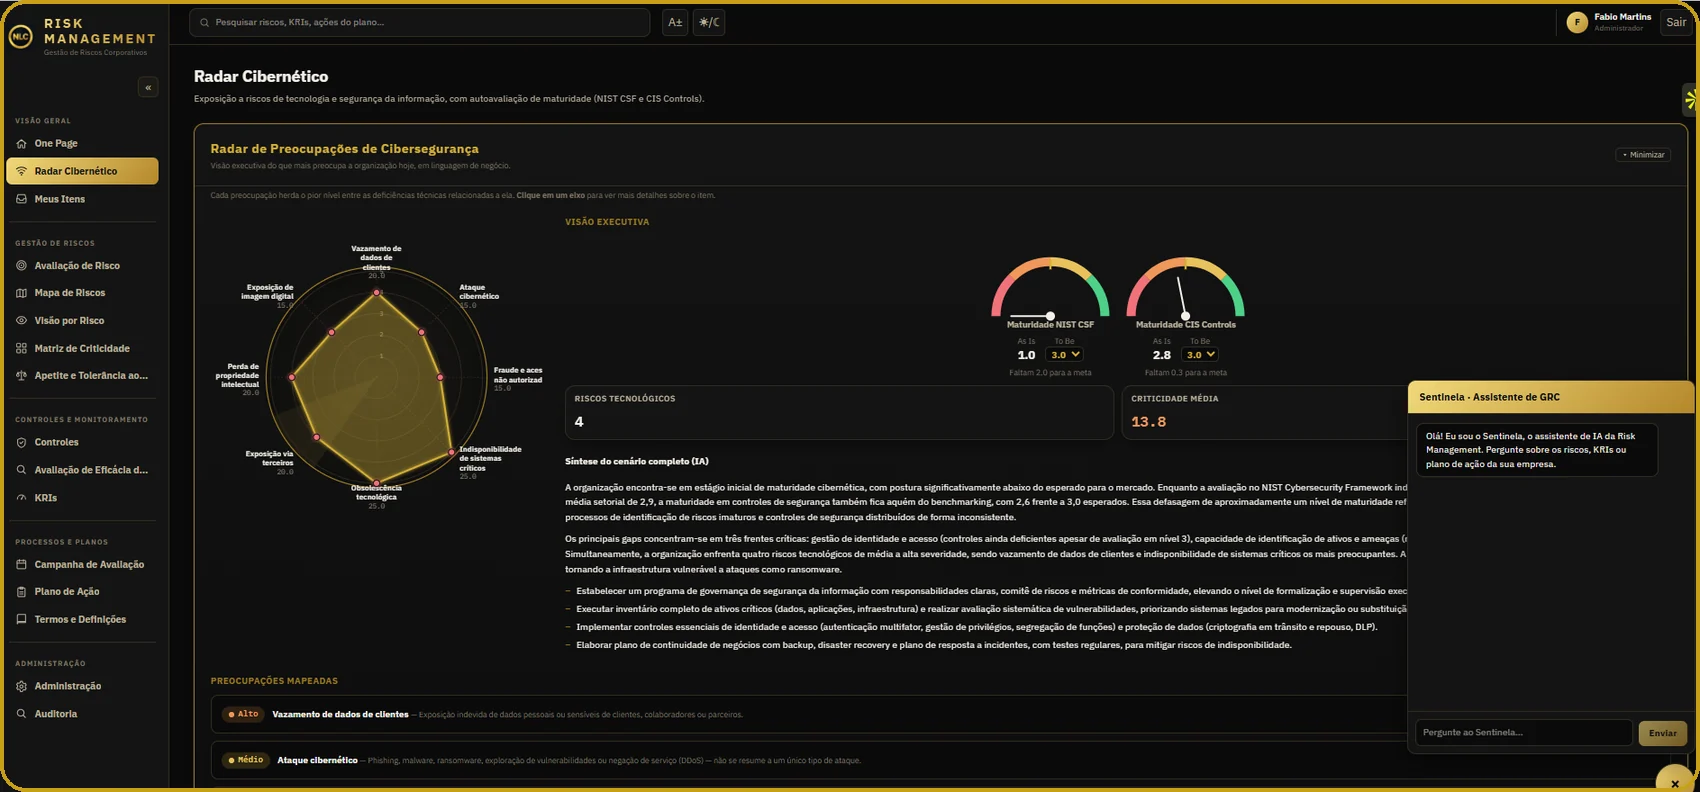
It happened? It's on record.
Section for materialized risks: event, impact and contingency.
- Dedicated section for materialized risks
- Event, impact and contingency triggered
- Basis to reassess risk and controls
- Event
- 18-hour terminal stoppage
- Impact
- Operational and financial
- Contingency
- Emergency reduction plan
- Reassessment
- Likelihood and controls revised
Illustration, fictitious data.
Ask for the report. Get it ready.
Reports in Word, PowerPoint or PDF, on your company template.
- Any topic, in Word, PowerPoint or PDF
- Structure tailored to the reader
- On your company's template and brand
- Key message
- Exposure × appetite
- Critical risks
- Decisions required
Board
Strategic, no jargon: key message, exposure × appetite, decisions.
Executives
Managerial: critical risks, KRIs out of bounds, plans and owners.
Managers
Operational: area risks, controls, actions and deadlines.
Audit
Technical and traceable: methodology, evidence and tests.
Security. At every layer.
Cloud
Market standards and redundancy.
Encryption
In transit and at rest.
Access
MFA, roles and least privilege.
Isolation
Each client in its own tenant.
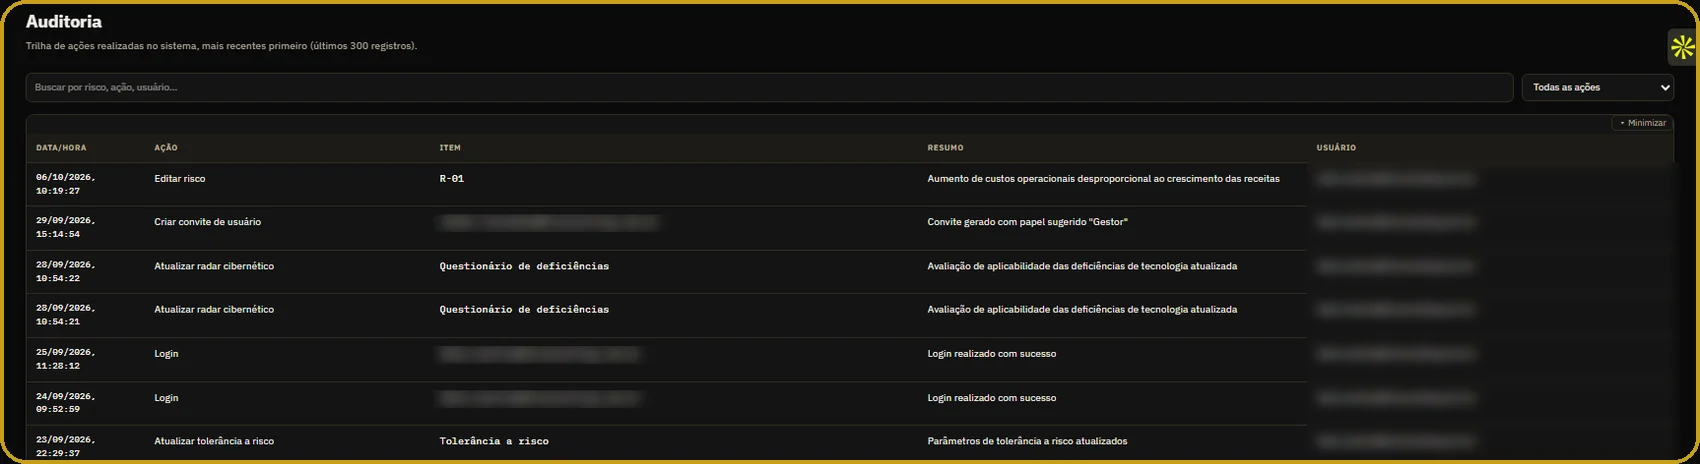
Trail
Every action logged.
LGPD
Incidents reported within 48h.
business days to go live.
Then 40 hours to get the platform running, with NLC consultants.
Choose your pace.
Annual
Save R$38,100/year.
- Full platform
- 12-month commitment
- Support and updates
Annual Advanced
Tailored.
- Full platform
- Up to 8h customization/mo
- 12-month commitment
Assisted Onboarding
R$ 9.997Extra hour
R$ 249Extra company
R$ 997Report Studio
R$ 997All plans include up to 10 named users, an AI allowance, support and updates. Report Studio sold separately. Prices in BRL, taxes included.
Built on the best standards.
COSO ERM and ISO 31000 → risk and controls · NIST CSF and CIS → Cyber Radar · IIA → audit
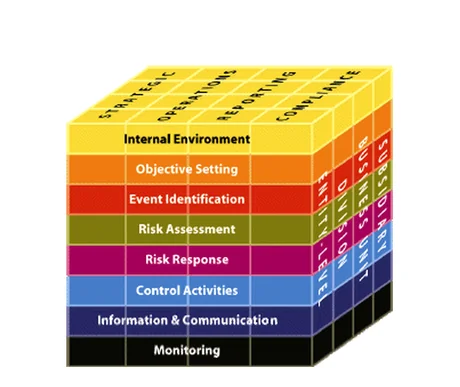 Internal Controls
 Risk Management
 Internal Audit
 Cybersecurity
 Hardening & Baselines
Want a closer look? Book a demo.
Guided demo with your own risk register.