Governance that leaves the paper. Governance you can prove.
Policies, committees, frameworks and AI models under one structure, traceable for the board, auditors and regulators.
 NLC | Governance
Illustration, fictitious data.
Before.
Expired policies in folders, minutes with untracked resolutions and compliance measured once a year.
Now.
Standards with owners and approval cycles, committees with agendas and resolutions, frameworks mapped to controls and evidence.
After.
The board can answer, with evidence, who decides what, including what AI decides.
IT, security, data, AI and crisis under one structure.
Policies and standards
Full lifecycle: drafting, review, approval, publication, attestation and expiry.
Committees and boards
Calendar, agendas, minutes, resolutions and tracking of what was decided.
RACI and authority
Single matrix of responsibilities and decision authority.
Multi-framework compliance
Requirements mapped to controls and evidence, one control serves many frameworks.
Compliance copilot
Interprets requirements, flags gaps and drafts the report.
Board dashboard
Consolidated governance exposure, in real time.
Who answers for what AI decides?
AI models already decide credit, fraud and hiring. NLC | Governance brings observability, explainability and an algorithmic audit trail, aligned with ISO/IEC 42001 and NIST AI RMF.
Model registry
Inventory, versions, owners and use cases.
Drift and bias
Performance and quality monitored in production.
Explainability
Algorithmic trail and natural-language explanations.
Approval and lifecycle
Approval policies, veto and human oversight.
One control. Many frameworks covered.
 IT Governance
 Information Security
 Continuity
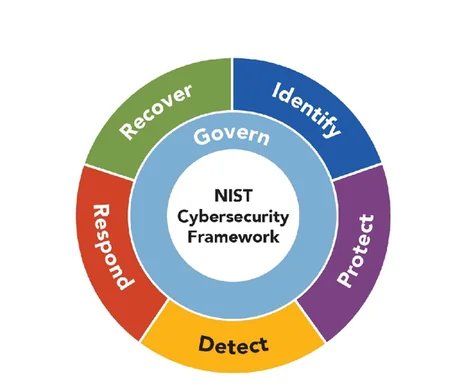 Cybersecurity
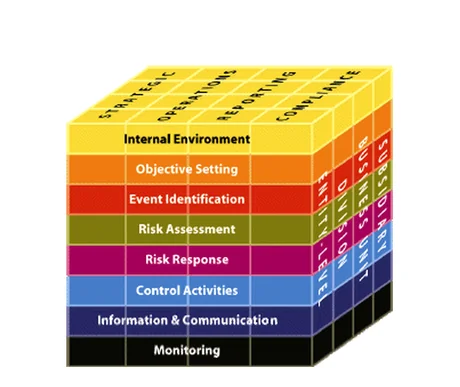 Internal Controls
Encryption
In transit and at rest.
MFA and roles
Least privilege by committee and area.
Audit trail
Every approval and resolution logged.
Isolated tenants
Multi-company, segregated.
Is your governance audit-proof?
Guided demo with your own policies and committees.